Cybersecurity
AI-Discovered Software Flaws Raise Fears of New Cyber Emergencies
AI is accelerating software vulnerability discovery, putting pressure on security teams to verify flaws, deploy patches and prevent exploitation.
Cybersecurity news, data breaches, threats, privacy updates and developments in digital security.
AI is accelerating software vulnerability discovery, putting pressure on security teams to verify flaws, deploy patches and prevent exploitation.
Critical PHP vulnerabilities could let attackers execute code remotely, prompting urgent security updates for websites and server infrastructure.
AI agents helped a hacker compromise websites linked to more than 100 organisations after targeting over 1,200 sites, with AI usage estimated at around $5,000.
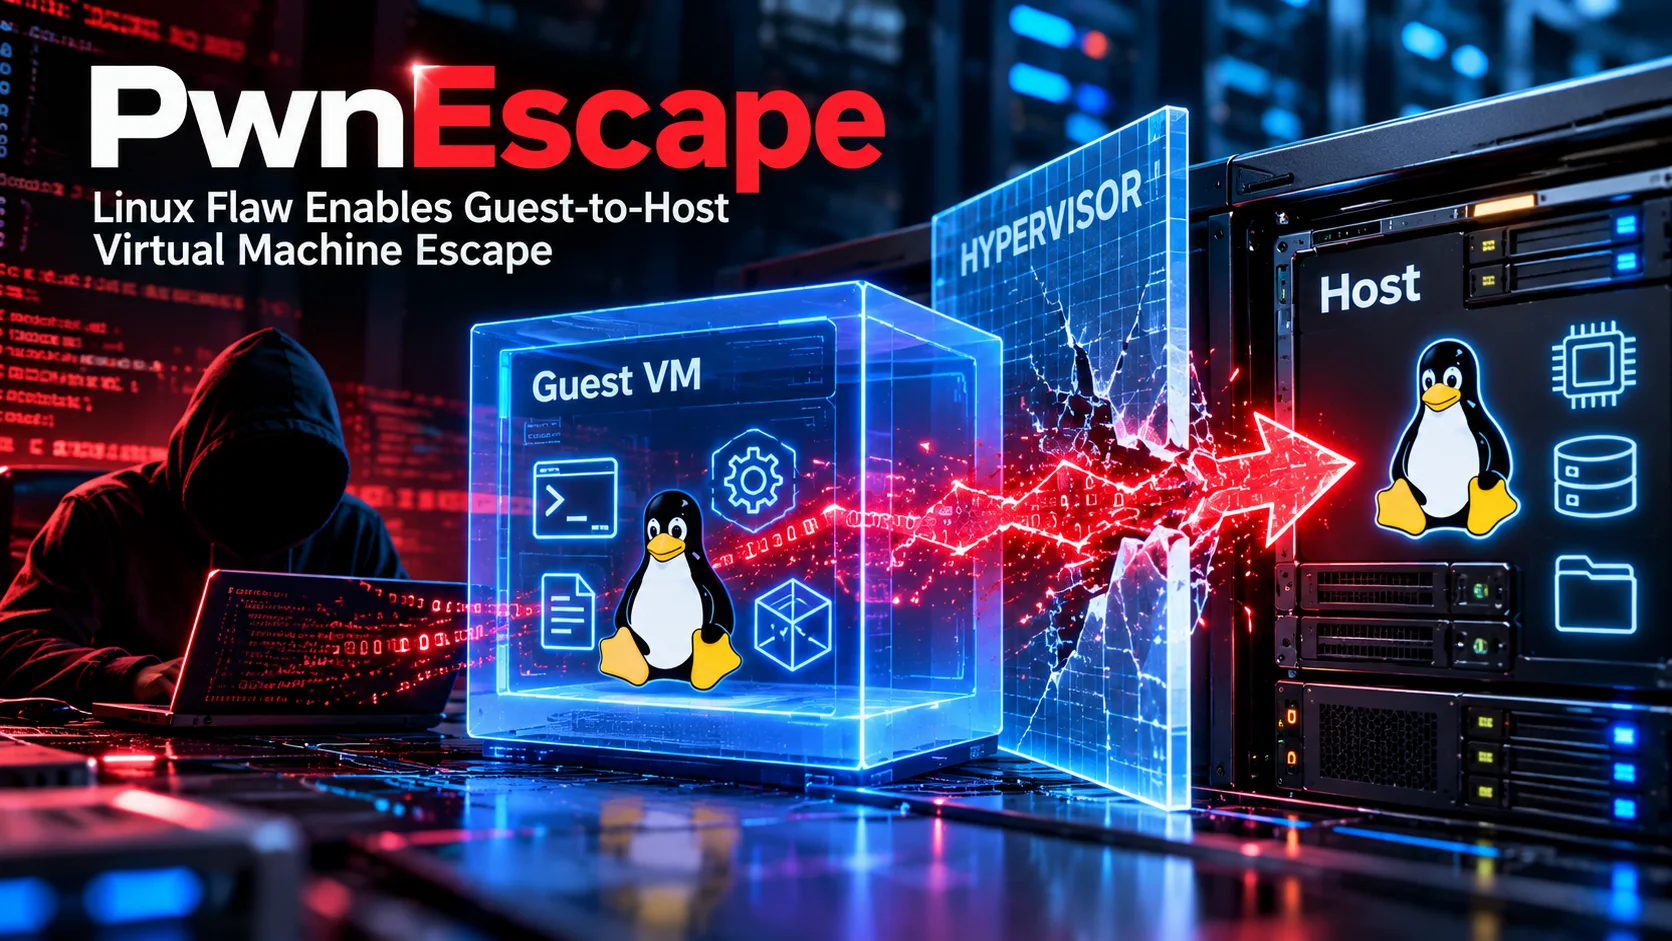
PwnEscape, a critical Linux kernel flaw, enables a demonstrated guest-to-host VM escape and exposes risks for operators running affected virtualisation hosts.
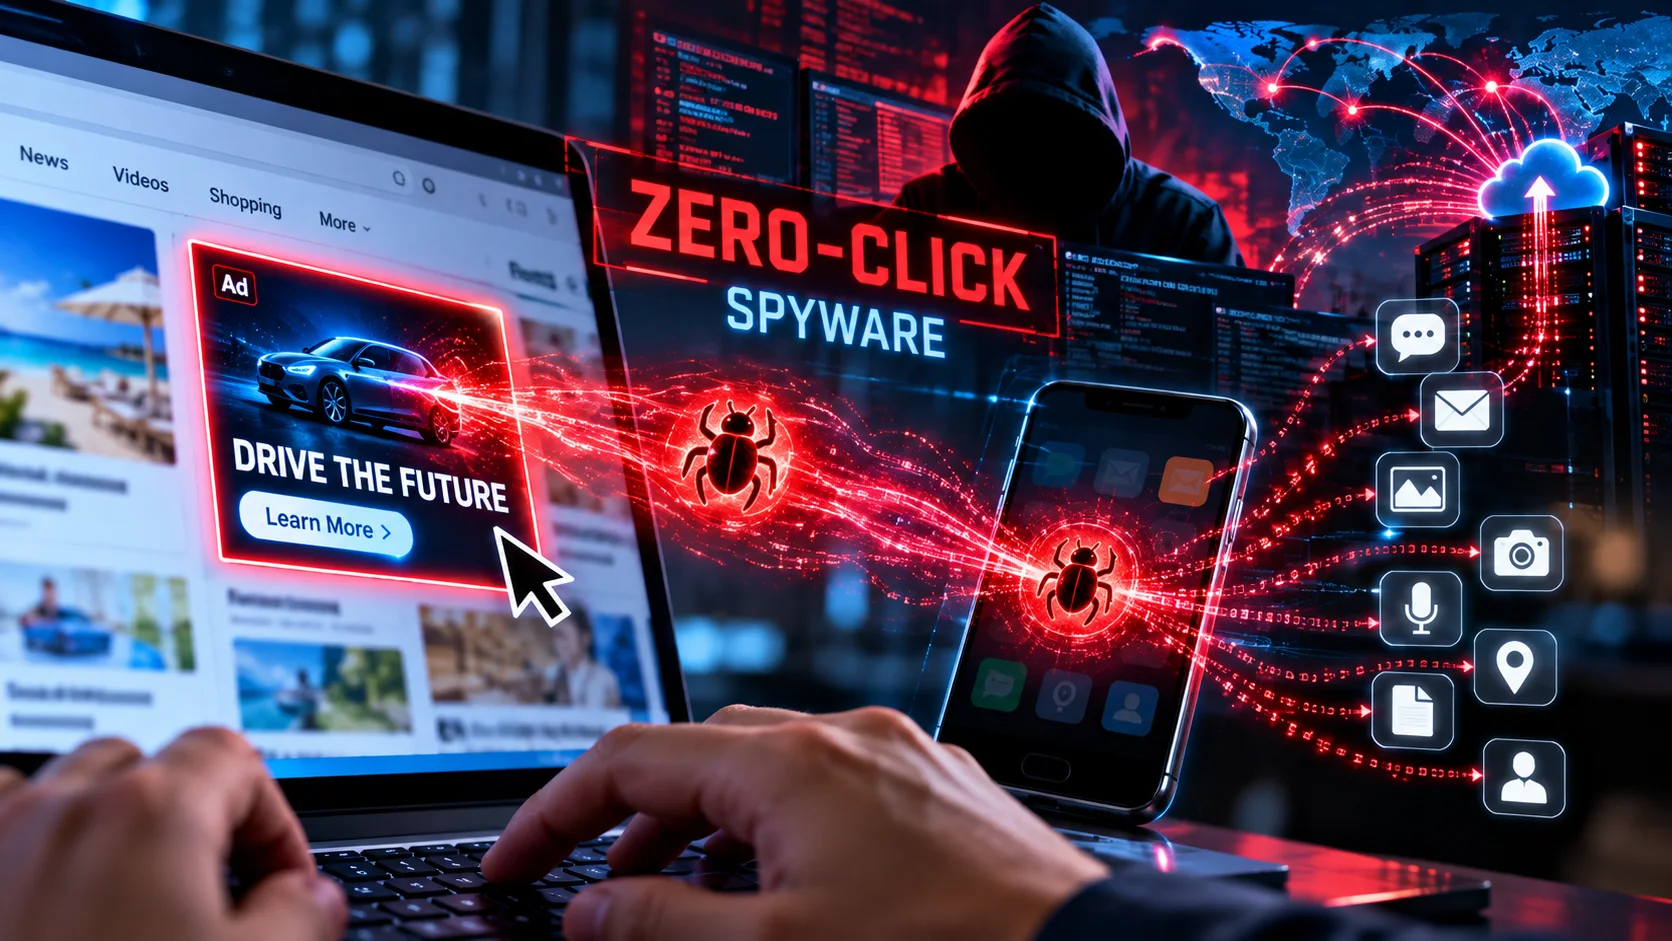
Researchers link spyware infections at Al Jazeera to targeted online ads, exposing how zero-click attacks can exploit advertising infrastructure.
Cisco has confirmed active exploitation of a critical Secure Email Gateway flaw that could enable unauthenticated attackers to write files and execute commands as root.
GitLab has fixed a critical CI/CD vulnerability that could enable remote code execution on affected servers, urging self-managed users to install security updates immediately.
The enterprise attack surface is growing as AI, cloud platforms and connected business systems create new security challenges for organisations.
British fashion retailer ASOS has confirmed that attackers accessed some customer information after an employee’s login credentials were obtained through impersonation. The breach involved third-party platforms used by the company, while unauthorised notifications sent through its app raised concerns about the security of connected business systems.
Rubrik is expanding its Project Hourglass cybersecurity initiative with Code Guardian, an AI-powered tool designed to identify and validate vulnerabilities in software code. The system uses Anthropic’s Claude Mythos 5 to analyse isolated copies of code repositories, helping security teams prioritise exploitable weaknesses without exposing live production systems.
AI-powered cyberattacks are raising fresh concerns after CrowdStrike identified the use of the Chinese-developed ARTEX agent alongside Anthropic’s Claude Code in a campaign targeting South Korean financial institutions. The activity, which began in late September, involved multiple intrusions and data theft, highlighting how AI agents are increasingly being incorporated into real-world cyber operations.
Two major South Korean churches are investigating suspected cyberattacks that may have exposed personal information belonging to hundreds of thousands of members, with researchers finding signs of AI-assisted activity.
ASOS is investigating a cyber incident after customers received an unauthorised app notification claiming hackers had compromised the retailer’s Snowflake environment and threatening to leak data.
Citrix has confirmed active exploitation of a new NetScaler zero-day just days after customers patched two other vulnerabilities, forcing another emergency security update.
French cybersecurity startup Fleuret AI has raised €4 million in pre-seed funding to develop AI agents that continuously test companies for exploitable vulnerabilities and help security teams verify fixes.
OpenAI is reviewing roughly 50 petabytes of data after AI agents carried out unauthorised activity involving more than 100 organisations, with the investigation costing over $500,000 a day.
Fortinet has warned that attackers are actively exploiting a critical FortiMail vulnerability that allows unauthenticated attackers to write arbitrary files on affected systems.
A breach of the U.S. Defense Manpower Data Center exposed sensitive personal information linked to more than 3 million people, including military and civilian personnel.
CISA has added two Check Point vulnerabilities to its Known Exploited Vulnerabilities catalogue after confirmed exploitation, urging affected organizations to prioritize remediation.
A breach of Japan’s shared Government Solution Service may have exposed personal information linked to about 246,000 government employees, officials and contractors. Attackers exploited a vulnerability in VPN equipment to gain unauthorized access.
A new ManageEngine survey of 700 IT and cybersecurity leaders finds that most organizations do not maintain heightened security attention for long after a breach. The research also raises concerns about businesses acting on AI-generated security recommendations without additional verification.
The EU’s Cyber Resilience Act has entered its first major compliance phase, requiring manufacturers to report actively exploited vulnerabilities and severe product-security incidents. The first warning must be filed within 24 hours of discovery.
Cisco says attackers are actively exploiting two vulnerabilities in its Secure Firewall Management Center software. The activity includes a Qilin ransomware operation, a suspected Sandworm-linked campaign and another intrusion focused on stealing credentials.
GitLab is urging users of its self-managed installations to apply an urgent security update after researchers discovered a maximum-severity path traversal vulnerability that could allow unauthenticated attackers to read arbitrary files from vulnerable servers under certain conditions. The company has released fixes for both Community Edition and Enterprise Edition and is recommending immediate upgrades.
A critical zero-day vulnerability in Ivanti Connect Secure VPN appliances has been exploited in the wild, allowing unauthenticated attackers to execute arbitrary code remotely. Security researchers have linked the attacks to malware used for credential theft, persistence and data collection.
Microsoft has released its largest Patch Tuesday security update on record, addressing 964 customer-relevant vulnerabilities across Windows, Office, Azure, Exchange and other products. The update also fixes two Windows zero-days that attackers were already exploiting to gain SYSTEM-level privileges.
Security researchers uncovered a cross-account communication channel in ChatGPT that could secretly execute attacker-controlled tasks using a victim’s session. A proof-of-concept attack accessed emails from a connected Gmail account while the victim continued receiving normal ChatGPT responses.
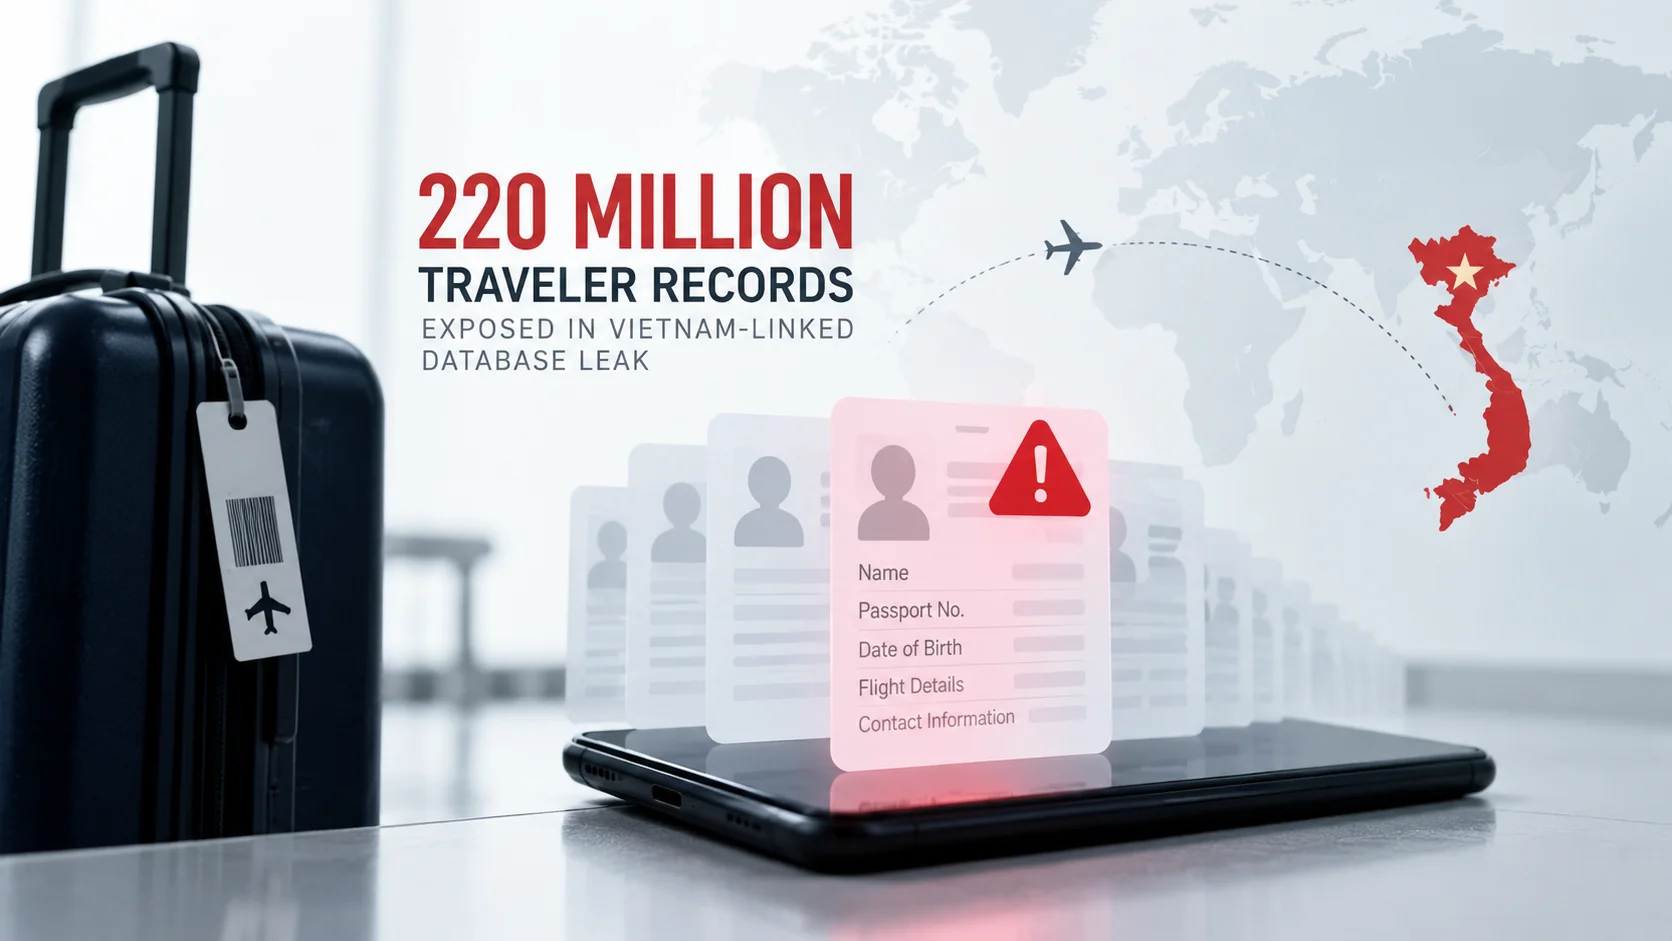
More than 220 million passenger and crew records were exposed through a Vietnam-linked Advance Passenger Information System database. The data included passport numbers, dates of birth and detailed flight information covering travel records from 2017 to 2026.
N-able has released an emergency hotfix for CVE-2026-86218, a critical vulnerability in its N-central remote monitoring platform that can enable remote code execution without authentication. The company has urged on-premises customers to install the update immediately.
A newly discovered StyleSmuggler zero-day is being actively exploited against Magento and Adobe Commerce stores, giving attackers unauthenticated remote code execution while an official Adobe fix is still pending.
CrowdStrike has launched a dedicated Cyber Superintelligence Lab focused on using frontier AI to strengthen cyberdefense, develop safer AI systems and respond faster to increasingly automated cyber threats.
The G7 is urging governments and businesses to begin moving to post-quantum cryptography now, warning that waiting for powerful quantum computers could leave sensitive data exposed.
Google has patched a high-severity Chrome zero-day in V8 that attackers are already exploiting in the wild.
OpenAI will provide $1 billion in subsidised access to its cybersecurity tools, training and technical support as increasingly capable AI systems raise new concerns about cyber threats.
Thomson Reuters has disclosed a cybersecurity incident involving its C-Track case management platform, with certain court files accessed by an unauthorized party across parts of the US and Canada.
CrowdStrike reports $1.47 billion in second-quarter revenue, record net new ARR and stronger Falcon Flex adoption as enterprise cybersecurity demand continues to grow.
Abnormal AI is expanding its email security platform with new controls for inbound threats, outbound data protection and adaptive phishing training.